
Oferta Exclusiva Idency:
MDR LIVRE
Malwarebytes: ThreatDown Elite including Managed Detection & Response for the price of ThreatDown Advanced
GRÁTIS Consultation com Malwarebytes engineer
Taking approx. 30 mins, you can speak with an expert to obtain the best advice on securing your network with an MDR overview.
GRÁTIS RDM com ThreatDown Advanced Bundle
To book your FREE consultation or start your FREE 30-day trial, please provide your email and we’ll get in touch:
Oferta Exclusiva Idency:
FREE MDR: ThreatDown Elite including Managed Detection & Response for the price of Advanced
ThreatDown Elite protection:
- A melhor solução de ransomware para empresas
- Proteção Antivírus de Próxima Geração Galardoada
- prevenção, deteção e resposta a ameaças geridas 24/7
- Melhorar a proteção e a conformidade de segurança
- Inclui reversão de ransomware de 72 horas (versão EDR)
ThreatDown Elite protection:
- Malwarebytes Award-Winning Next-Gen Antivirus Protection
- prevenção, deteção e resposta a ameaças geridas 24/7
- Melhorar a proteção e a conformidade de segurança
- Inclui reversão de ransomware de 72 horas (versão EDR)
- A melhor solução de ransomware para empresas
GRÁTIS Consultation com ThreatDown engineer e 30-Day FREE Trial
To book your FREE consultation or start your FREE 30-day trial, please provide your email and we’ll get in touch:
ThreatDown Advanced Bundle com MDR GRATUITO
Deteção e Resposta Geridas (MDR) is a Malwarebytes service that offers round the clock monitoring of your IT infrastructure by an expert cybersecurity team. 24hrs a day – 365 days a year.
Obtenha Cotação ExclusivaThreatDown Advanced:
- Resposta a incidentes
- Antivírus de nova geração
- Controlo de dispositivos
- Bloco de Aplicação
- Avaliação de Vulnerabilidades
- Reversão de Ransomware
- Deteção e Resposta ao Nível do Ponto Final
- Gestão de Correções
- Investigação de Ameaças Gerida
ThreatDown MDR:
- Menor pressão sobre as equipas de TI existentes
- 24/7 monitoring from security experts
- Maior segurança a um custo reduzido
- Managed threat detection & response
- Faster response & remediation times
- 99% less risk of successful breach
- Faster response & less impact
- Zero falsos alertas
- Tranquilidade de espírito
FAST FORWARD with ThreatDown MDR by Malwarebytes
FAST FORWARD with ThreatDown MDR
Cybercriminals don’t take time off during holidays and weekends, and even see them as the ideal time to target small and large businesses. To combat 24×7 threats, you need 24×7 security. However many organisations lack the funds, staff, and expertise necessary for delivering 24hr security services.
ThreatDown MDR is an easy, efficient, cost-effective way to detect and respond to threats. Offering 24/7 monitoring, threat hunting, and remediation carried out by experienced security experts. Your organisation can achieve faster response and remediation times, at significantly less cost.
Start 30-Day FREE Trial
How ‘cyberwhelmed’ is your organisation?
How ‘cyberwhelmed’ is your organisation?
Questions for your security team:
- Does your IT lack the staff, skill and budget for 24×7 security?
- Is your IT overwhelmed by constant alerts?
- Is your IT busy with other tasks aside from cybersecurity
- Is your alert response time below average?
- Are you unsure if your organisation meets compliance standards?
If the answer to any of these you answered yes to any of these questions then partnering with an MDR provider might be the solution for you.
Para um tempo limitado apenas, a Idency está a oferecer a novos clientes a ThreatDown Advanced pacote com GRÁTIS Deteção e Resposta Geridas (MDR).
Request FREE ConsultationCompre 2 anos, leve o 3.º GRÁTIS
Built for everyone, Malwarebytes Soluções ThreatDown combinar tecnologia com serviços para proporcionar uma proteção robusta que seja eficiente e económica. Com um pacote de segurança adequado à dimensão e às necessidades de qualquer organização:
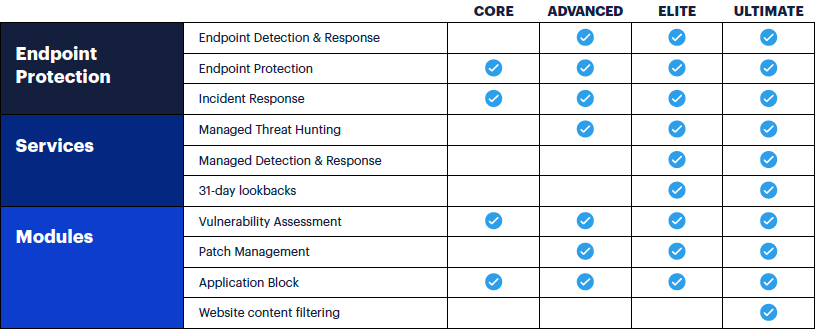
| Funcionalidade | Núcleo | AVANÇADO | ELITE | MÁXIMO |
|---|---|---|---|---|
| Deteção e Resposta ao Nível do Ponto Final |  | | | |
| Proteção de Endpoints | | | | |
| Resposta a Incidentes | | | | |
| Investigação de Ameaças Gerida | | | | |
| Detecção e Resposta Geridas | | | ||
| Análises retrospetivas de 31 dias | | | ||
| Avaliação de Vulnerabilidades | | | | |
| Gestão de Correções | | | | |
| Bloco de Aplicação | | | | |
| Filtragem de conteúdos de websites | |
Tome medidas hoje com os nossos serviços abrangentes de cibersegurança e proteja a sua empresa contra a ameaça constante de ransomware. Para mais informações sobre os disponíveis Pacotes de segurança ThreatDown, por favor entre em contacto ou dê uma vista de olhos na nossa Visão geral do ThreatDown página.
Entre em contactoSelecting an MDR Provider
When selecting a Managed Detection and Response (MDR) provider, a company should consider the following key factors:
1. Comprehensive Threat Detection Capabilities
- Threat Intelligence Integration: The MDR provider should use threat intelligence feeds to stay updated on the latest threats.
- Advanced Detection Techniques: Look for capabilities like behavioural analysis, machine learning, and anomaly detection to identify sophisticated threats.
- Endpoint Visibility: Ensure the provider offers in-depth visibility into endpoints, including remote and IoT devices.
2. 24/7 Monitoring and Response
- Always-On Service: The MDR provider should offer round-the-clock monitoring to respond to threats anytime.
- Rapid Incident Response: Ensure they provide quick response times, with SLAs that specify response duration for various types of incidents.
3. Customisable and Scalable Solutions
- Tailored Services: The provider should be able to adapt their services to your specific business needs, including industry regulations.
- Escalabilidade: Ensure the MDR can grow with your business, accommodating new users, systems, and increasing data volumes.
4. Integration with Existing Infrastructure
- Compatibilidade: The MDR solution should integrate seamlessly with your existing security tools (e.g., SIEM, firewalls, antivirus).
- Cloud Support: If your company uses cloud services, ensure the provider supports cloud environments and hybrid infrastructures.
5. Proven Track Record and Expertise
- Experience and Certifications: Look for a provider with a proven history of success, industry certifications (such as ISO 27001), and expertise in various industries.
- References and Case Studies: Ask for client references and case studies to gauge customer satisfaction and service reliability.
6. Incident Response Playbooks and Automation
- Well-Defined Playbooks: The provider should have predefined incident response playbooks for different types of threats.
- Automation: Look for capabilities that automate repetitive tasks, accelerating response and reducing human error.
7. Threat Hunting Services
- Proactive Threat Hunting: Ensure the MDR provider offers proactive threat hunting to identify potential threats that traditional detection may miss.
- Specialised Expertise: The team should have dedicated security analysts with skills in advanced threat hunting.
8. Communication and Reporting
- Clear Communication Channels: There should be easy-to-use communication channels for collaborating during incident response.
- Regular Reporting: Look for detailed reporting that includes metrics, threat summaries, response actions, and recommendations to improve your security posture.
9. Compliance and Regulatory Support
- Compliance Expertise: Ensure the provider understands relevant regulations (e.g., GDPR, HIPAA) and can help your organisation meet compliance requirements.
- Audit Support: The MDR should offer assistance in providing evidence and reporting during audits.
10. Cost and Contract Flexibility
- Preços transparentes: Look for transparent pricing that outlines the services included to avoid unexpected costs.
- Flexible Contracts: Seek contract flexibility that allows you to scale services up or down and avoid long-term commitments without clear value.
11. Service Level Agreements (SLAs)
- Defined SLAs: Ensure the MDR provider offers SLAs with clear metrics, including response times, availability, and escalation processes.
- Accountability: SLAs should hold the provider accountable for delivering on their commitments effectively.
12. Client Onboarding and Support
- Smooth Onboarding: The onboarding process should be well-defined to minimize disruption to your business.
- Ongoing Support: Look for a provider that offers continuous support, including technical help, account management, and periodic reviews of your security posture.
A combination of these factors can help ensure you choose an MDR provider that effectively meets your organisation’s needs, enhances your cybersecurity posture, and aligns with your business goals.
You may also be interested in reading our white paper, Is MDR Right for Your Organisation?
Oferta Exclusiva Idency:
MDR LIVRE com o ThreatDown Advanced
FREE consultation with ThreatDown expert and 30-day FREE trial
To book your FREE consultation or start your FREE 30-day trial, please provide your email and we’ll get in touch:
 English (UK)
 English
 English (Canada)
 Français du Canada
 Svenska
 Português
 Nederlands
 Italiano
 Français
 Español
 Deutsch